The same evidence, mapped straight onto the frameworks that matter
Cyber Essentials, UK GDPR, NCSC 10 Steps, NIST CSF, ISO 27001 and SOC 2: one underlying baseline, six live compliance scores, no separate audit exercise.
Framework compliance is usually a once-a-year bolt-on
Cyber Essentials, ISO 27001, GDPR: for most MSPs and their clients, "compliance" means a spreadsheet audit done once a year, disconnected from the day-to-day IT work, and stale the moment it's finished. Nobody knows the real position between audits.
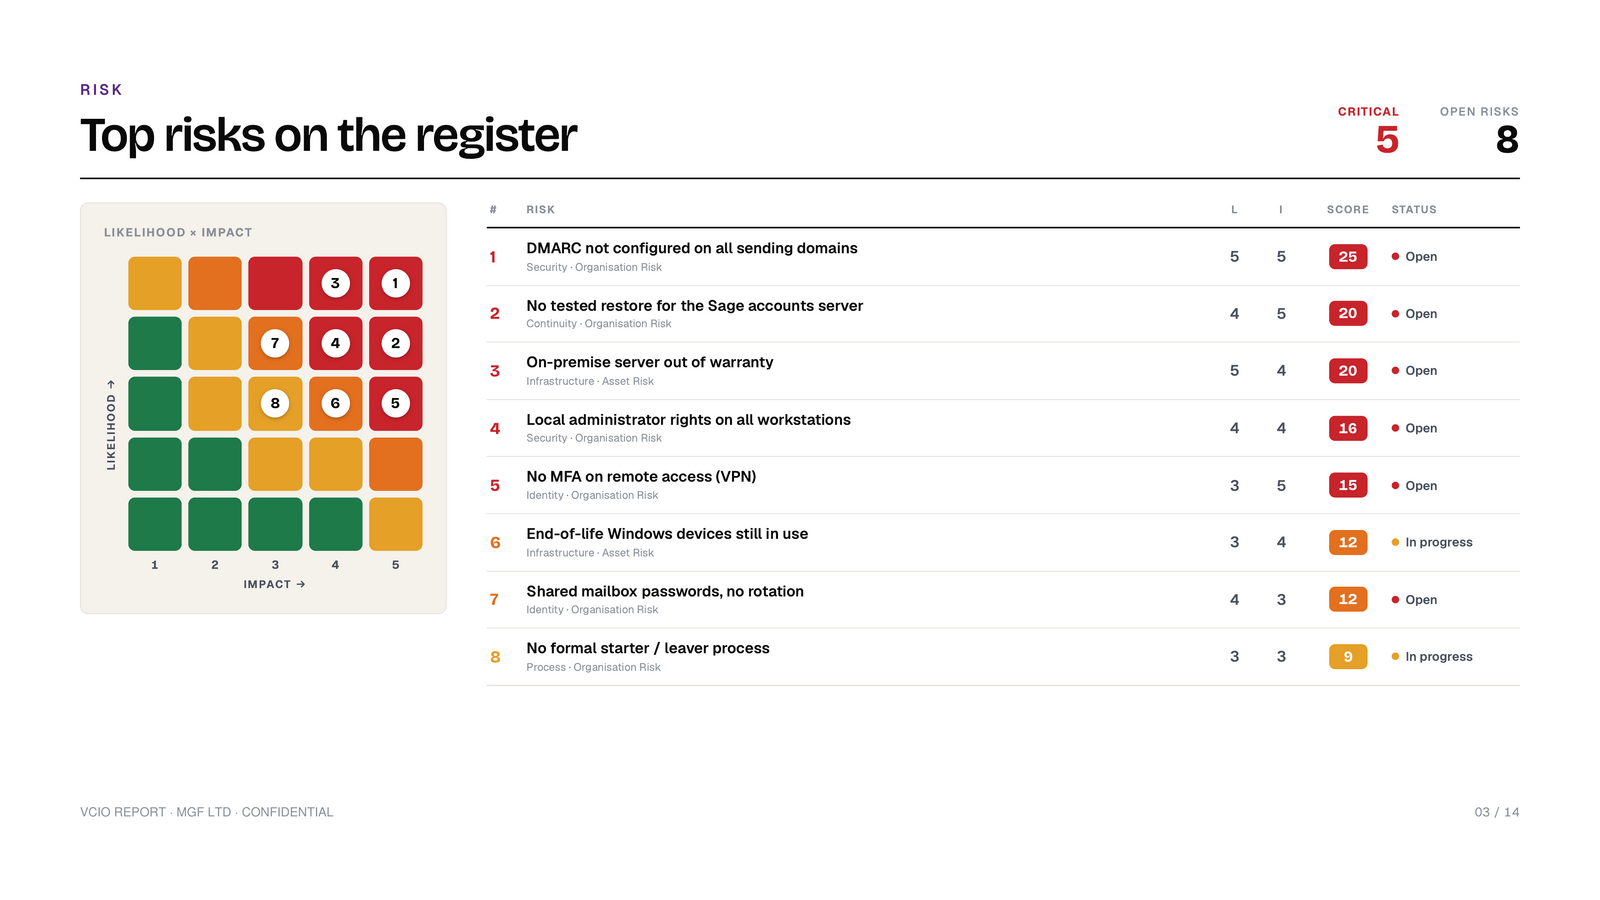
Example output from a demo account, not a real customer's data.
Six frameworks, scored live from the same data
The same Standard Library data that scores general alignment is re-expressed against each framework's actual control and policy requirements, so compliance status updates automatically as the underlying baseline improves, with no separate exercise.
- Cyber Essentials, UK GDPR / Data Protection Act 2018, NCSC 10 Steps to Cyber Security
- NIST Cybersecurity Framework 2.0, ISO/IEC 27001:2022, SOC 2 (Trust Services Criteria)
- Live % match per framework, with controls and policies counted explicitly, not a vague score
- Shows exactly what's outstanding, so the nearest certification is obvious
Example output from a demo account, not a real customer's data.
Know which framework is worth chasing first
Instead of guessing, you can see exactly which framework is closest to achievable and prioritise real certification work around it, with the same evidence supporting the client conversation and, if they go for it, the actual audit.
- Always know which framework is nearest to certification
- One compliance view instead of a separate spreadsheet per framework
- Feeds the same conversation as Risk Register and the roadmap, not a bolt-on report
See where your clients stand against these six
Book a walkthrough and we'll show a real (or sample) client's position across Cyber Essentials, ISO 27001 and the rest.
Book a demo